





Zum Inhalt springen
Factsheets
Concise knowledge for the Board of Directors and Executive Management. Enter your details to download the factsheets as PDFs.
First name
We treat your details confidentially. Details in our Privacy Policy.
Newsletter
Stay informed: receive current assessments of risk, security and compliance straight to your inbox. Free of charge, unsubscribe at any time.
First name
We treat your details confidentially and use them solely to send the newsletter. You can unsubscribe at any time. Details in our Privacy Policy.

Contact

You will be scrutinised either way. The only question is by whom first.

Whether regulator, EU client or insurer: the question of evidence will come. Better to answer it yourself first. Briefly describe your situation and I will get back to you personally.

Direct line

Risk Control RCC GmbHAlte Badenerstrasse 25CH-8173 Neerach
I will get back to you personally within two working days. Your details remain confidential, under NDA on request. In the event of an acute security incident, please call directly: +41 78 880 98 48.

Required fields are marked with *.

Details zur Bearbeitung Ihrer Angaben: Datenschutzerklärung

Skip to content

For Boards of Directors, Executive Management, Heads of IT & CISOs · Switzerland and the EU

NIS-2 isn’t liable.
You are.

Risk assessment, penetration testing, regulation and crisis response for Boards of Directors, Executive Management, Heads of IT and CISOs – independent of software and product vendors, confidential, under NDA on request. Through your EU subsidiary, as a supplier to a regulated client or as an IT service provider to a bank: NIS-2 and DORA reach Swiss companies faster than most board minutes suggest.

Acute security incident? Emergency contact →
  • Confidential, under NDA on request
  • Independent of software and product vendors
  • Based in Neerach / Zurich since 2003
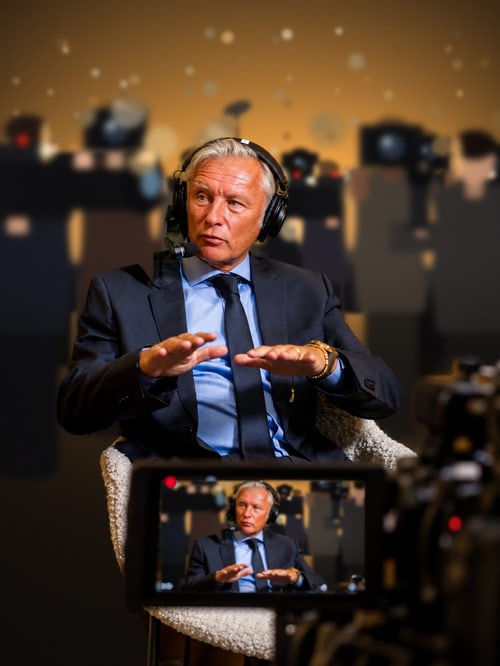
Prof. Dr. Richard Werner · Managing Director, Risk Control RCC GmbH · 30 years of governance, risk & compliance, BCM and crisis management

Playing the video loads it from YouTube (Google), which transmits data to Google. More in our Privacy Policy.

▶ Watch video with sound (in German)
Evening atmosphere over Zurich with the Grossmünster, Lake Zurich and the Alps
FrameworksNIS-2 (EU) 2022/2555DORA (EU) 2022/2554BSIG (DE)NISG 2026 (AT)ISA (CH)FINMA Circ. 2023/1ISO 22301ISO/IEC 27001BSI 200-4TISAX

Trusted at the highest level

Those who bear responsibility rely on experience.

Client logos: Bumrungrad International Hospital, Mayo Clinic, Mahidol University Faculty of Medicine Siriraj Hospital, Bangkok Hospital, Singapore General Hospital, AKH, Universitätsspital Zürich, Inselspital, Klinik Hirslanden, Spital Region OberaargauClient logos: Helsana, Sanitas, Bergwald Projekt, Kantonsspital Baden, Chur, Bénédict, Kreuzlingen, Academia Engiadina, Gemeinde Riehen, BVS Business-School Switzerland
Client logos: Universität Zürich, Cendres+Métaux, ETH Zürich, Endress+Hauser, Universität St.Gallen, KE, SIG, Axel Springer, Autogrill, Steinhoff International HoldingsClient logos: Bouygues Energies & Services, NorteShopping, Axpo, Colombo, Pfiffner, Continente, Bodensee-Arena, UBS Schweiz, Helvetia, Rothschild
Client logos: Swiss Re, Leumi, Zurich, Die Post, Swiss Life, St.Galler Kantonalbank, Krungsri, Graubündner Kantonalbank, SCB, RBSClient logos: Grand Casino Luzern, Coutts, Grand Casino Baden, Kempinski, Giardino Hotels Switzerland, Atlantis by Giardino Zürich, Glockenhof Zürich, Starwood Preferred Guest, Motel One

WHO IT’S FOR

Four roles. One responsibility.

Cyber risks do not land with IT alone. Each role needs a different answer – and all of them need the same evidence.

Board of Directors

Your duty of care – evidenced, not merely asserted.

Responsibilities, risk appetite and reporting lines set up so that the Board of Directors can evidence its duty of care (CO Art. 716a).

  • NIS-2 Resilience Check
  • Strategic GRC advisory
  • Formats for governing bodies
Book an initial consultation →
Executive Management

Able to decide when the clock is ticking.

Under NIS-2, the early warning to the authority is due within 24 hours. By then it must be clear who decides and what is protected first.

  • Cyber Security Crisis Response
  • Ransomware Response
  • Business Impact Analysis
Book an initial consultation →
Head of IT

Know where you are vulnerable – before others do.

Identify vulnerabilities and attack surfaces and prioritise them by business impact – in IT and OT.

  • Risk Assessment
  • Penetration Testing
  • Deep Scan
  • OT Risk Assessment
Request an assessment →
CISO

The evidence for Executive Management, regulators and clients.

Test whether your defences hold in an emergency, and prepare the results so that they stand up before regulators and clients.

  • Red Teaming vs. Blue Teaming
  • AI Risk Assessment
  • NIS-2, DORA, TISAX, ISO/IEC 27001
Request a Resilience Check →

The situation

Why waiting is no longer an option for the Board and Executive Management

Switzerland is no special case as soon as an EU client, an EU subsidiary or a regulated principal is involved. Three risks then land not with IT, but at the boardroom table.

€10 m

Liability and law

Responsibility lies with individuals, not with the IT department

NIS-2 requires management bodies to approve and oversee cybersecurity risk-management measures (Art. 20). For essential entities, fines reach up to €10 m or 2 % of total worldwide annual turnover (Art. 34). Anyone who cannot prove they paid attention bears the risk personally.

Art. 21

Lost business in the supply chain

Your EU client asks for evidence, not good intentions

Art. 21 NIS-2 and Art. 28 to 30 DORA oblige regulated clients to assess their suppliers and bind them contractually. Those who cannot provide the evidence are not rejected at the next tender – they are not even invited.

24 h

Standstill without a BIA

In an emergency, sequence counts, not intention

The early warning to the authority is due within 24 hours (Art. 23). Without a Business Impact Analysis, you will not know in that time which processes must be rescued first, how long they may be down and who decides.

You don’t repaint the funnel of a sinking ship. You check whether there are enough lifeboats – before you cast off.
Check whether you are affected now

SERVICES · ASSESSMENT AND TESTING

How vulnerable are you really?

Your company assessed through the eyes of an attacker – and the findings translated into decisions for Executive Management.

Risk Assessment

Threats, vulnerabilities and impacts on your critical processes assessed – linked to the Business Impact Analysis.

    Outcome: risk picture and prioritised action plan.

    Penetration Testing

    Controlled attacks on networks, applications and systems – within the agreed scope and with written authorisation.

      Outcome: findings with ratings and recommendations, plus a summary for Executive Management.

      Red Teaming vs. Blue Teaming

      Red Teaming plays a realistic attacker, Blue Teaming strengthens detection and defence. Together they show whether your defences hold in an emergency.

        Outcome: attack paths, detection gaps, improved procedures.

        Deep Scan

        Comprehensive analysis of your attack surface and vulnerabilities, prioritised by business impact.

          Outcome: prioritised list of vulnerabilities.

          AI Risk Assessment

          Where do you use AI, which data flows, who decides? Risks such as data leakage, manipulation and a lack of governance are assessed.

            Outcome: AI risk profile and governance recommendations.

            OT Risk Assessment

            Production, control and building technology: identifying risks without jeopardising operations.

              Outcome: OT risk picture and action plan.

              Scope, methods and deliverables are agreed for each engagement.

              Request an assessment →

              CRISIS RESPONSE

              When the incident strikes, the crisis team leads – not panic.

              Whether ransomware or data leakage: support for your crisis management team with decisions, notifications and recovery.

              Cyber Security Crisis Response

              Lead decisions, communication and notifications to the authorities in a structured way. NIS-2: early warning within 24 hours. Switzerland: reporting of cyberattacks on critical infrastructure to the Federal Office for Cyber Security (BACS) within 24 hours.

              Ransomware Response

              Coordinating initial measures, steering recovery according to the priorities of the Business Impact Analysis, and supporting coordination with authorities and communication.

              Preparation

              Crisis playbooks for ransomware, supplier failure, data leakage and blackout. Tabletop and command-post exercises for the crisis management team.

              Acute security incident?

              Call directly: +41 78 880 98 48

              REGULATION AND STANDARDS

              Meet obligations. Provide evidence.

              Preparation for audit, assessment and certification – pragmatic and documented so that it stands up before regulators and clients.

              NIS-2 (EU) 2022/2555

              Determining applicability, gap analysis against Art. 21, training of management bodies under Art. 20.

              DORA (EU) 2022/2554

              Implementation for financial entities and ICT third-party service providers, management of third-party providers.

              TISAX

              Preparation for the TISAX assessment in the automotive supply chain.

              ISO/IEC 27001

              Preparation for certification of the information security management system.

              ISO 22301 and BSI 200-4

              Business continuity management, Business Impact Analysis and contingency planning.

              ISO 22361

              Establishing and exercising the crisis organisation.

              ISA (CH)

              Reporting process for cyberattacks on critical infrastructure.

              FINMA Circ. 2023/1

              Operational resilience in the financial sector.

              Risk Control RCC supports preparation and implementation. Certifications and assessments are carried out by accredited bodies.

              Check whether you are affected now →

              The entry offer

              Clarity first. Then budget.

              Within a few weeks, the NIS-2 Resilience Check answers the question that no one on the Board can answer with certainty today: Are we affected, where do we stand, and what needs to be done next? It consists of two modules that build on each other.

              Module A

              NIS-2 Qualification

              You find out definitively whether and in what role NIS-2 or DORA covers your company – directly, through an EU subsidiary or as a supplier.

              • Applicability analysis by sector, size and supply relationships
              • Classification of your role: essential or important entity, supplier, ICT third-party service provider
              • Clear statement on deadlines and reporting obligations
              Module B

              NIS-2 Resilience Check

              A gap analysis against the requirements of Art. 21 that shows where your organisation stands today – and what a regulator or client would see first.

              • Assessment of governance, risk management, supply chain and incident process
              • Alignment with your existing ISO certifications and security measures
              • A prioritised action roadmap instead of a 200-page paper tiger
              What you hold in your hands at the end
              ClarityWhether and how you are affected
              Gap analysisWhere the gaps to Art. 21 lie
              RoadmapWhat needs to be done, in which order
              Basis for decisionA paper for the Board of Directors
              Request a NIS-2 Resilience Check

              We discuss scope and terms in the first conversation. Confidential, under NDA on request.

              SERVICES · LEADERSHIP AND GOVERNANCE

              Three disciplines, one programme

              Governance sets the direction, implementing NIS-2 and DORA provides the evidence, and the Business Impact Analysis carries you through an emergency. I bring all three together so that they do not end up as three separate projects.

              I

              Strategic GRC advisory

              Governance as an instrument of leadership and protection

              Responsibilities, risk appetite and reporting lines are set up so that the Board of Directors and Executive Management can evidence their duty of care (CO Art. 716a).

              • Risk and control framework for the Board and Executive Management
              • Reporting that documents decisions
              • Integration of risk, compliance and business continuity
              II

              NIS-2 and DORA implementation

              Pragmatic, for regulated companies and suppliers

              Requirements are translated into measures that suit your organisation and documented so that they withstand scrutiny by regulators or clients.

              • Measures under Art. 21 NIS-2 and Art. 5 DORA
              • Management of suppliers and ICT third-party service providers
              • Incident process and reporting channels
              III

              Business Impact Analysis

              The foundation of true resilience

              Critical business processes, their dependencies and tolerable downtimes are identified. From this follow priorities for protection, recovery and investment.

              • Critical processes, dependencies and RTO/RPO
              • Prioritisation of investment by business impact
              • Basis for contingency and crisis organisation (ISO 22301)

              Why Risk Control RCC

              Neither paper opinions nor product sales

              Large law firms deliver legal opinions, system integrators deliver tools. In between, the question of how a company actually acts in an emergency remains unanswered. That is exactly where I work.

              Large law firm System integrator Risk Control RCC
              Focus Legal interpretation Technology and products Management responsibility and operational crisis practice
              Outcome Opinions and memoranda Implemented solution Demonstrable programme with action roadmap
              Independence High Tied to own portfolio Independent of software and product vendors
              Point of contact Changing teams Project manager Me personally, with experts from my network
              Portrait of Prof. Dr. Richard Werner

              Prof. Dr. Richard Werner

              Managing Director, Risk Control RCC GmbH

              30 years of experience in governance, risk & compliance, business continuity and crisis management. Professor of business, studied at Stanford and in Vienna, keynote speaker. Behind Risk Control RCC stands a network of experienced senior experts, whom I assemble according to the task.

              What matters is not predicting the future, but being prepared for it.Attributed to Pericles
              Experience in regulated industries and critical infrastructure
              • Banks and financial services providers
              • Insurance
              • Energy and utilities
              • Healthcare
              • Industry and suppliers
              • Public sector

              The approach

              In three steps from suspicion to demonstrable compliance

              1

              Qualification and Resilience Check

              We clarify whether and how you are affected, and measure your status against the requirements. Outcome: gap analysis and a basis for decision for the Board of Directors.

              2

              Business Impact Analysis and roadmap

              We identify your critical processes and their dependencies and derive a prioritised roadmap from them. Outcome: you know what must be protected first and what it costs.

              3

              Sustainable GRC integration

              Measures, responsibilities and reporting lines are embedded in your organisation and practised together. Outcome: a programme that runs day to day and holds in an emergency.

              The best players are of no use if the team has not trained to play together with discipline. Resilience is an exercise, not a document.

              Start with step 1

              VIDEO

              NIS-2 qualification and resilience

              The essentials in a few minutes: applicability, management’s obligations and the path to demonstrable compliance.

              Playing the video loads it from YouTube (Google), which transmits data to Google. More in our Privacy Policy.

              The objections

              Four questions decision-makers ask me first

              We are based in Switzerland. Why does NIS-2 still affect us?

              NIS-2 applies to entities within the EU. You are nonetheless affected if you operate an EU subsidiary, provide services in the EU or, as a supplier to a regulated client, must meet its supply-chain requirements. The same applies to DORA for financial entities and their ICT service providers. The qualification establishes definitively whether, and in what role, this applies to you.

              Isn’t our existing ISO certification or IT security enough?

              It is a good foundation, but rarely sufficient. ISO 27001 or ISO 22301 cover many requirements, but not automatically the responsibility of management bodies, the reporting deadlines or supply-chain management under Art. 21 NIS-2. The Resilience Check shows what you already meet and where specific gaps remain.

              What does getting started cost, and how long does it take?

              Scope and duration depend on the size, structure and supply relationships of your company. In the first, non-binding conversation I will give you a clear framework before you commit.

              How confidentially do you treat our information?

              On request, we work under NDA from the outset. I work independently of software and product vendors and do not pass any data on to third parties. Any experts from my network who are brought in are likewise bound to confidentiality.

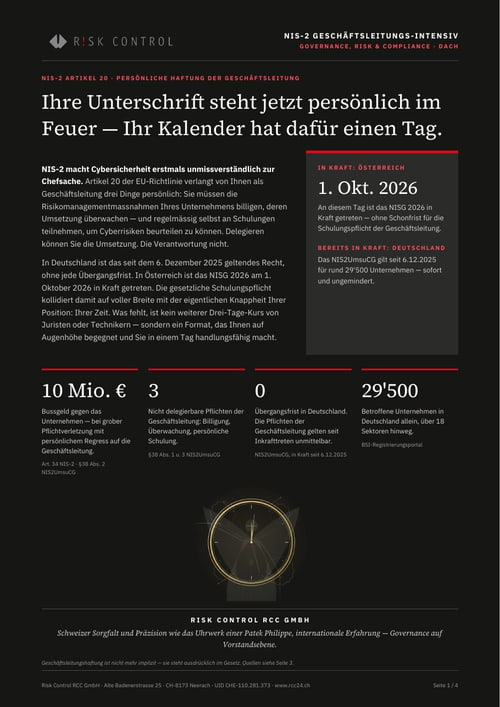
              Factsheet NIS-2 Executive Intensive
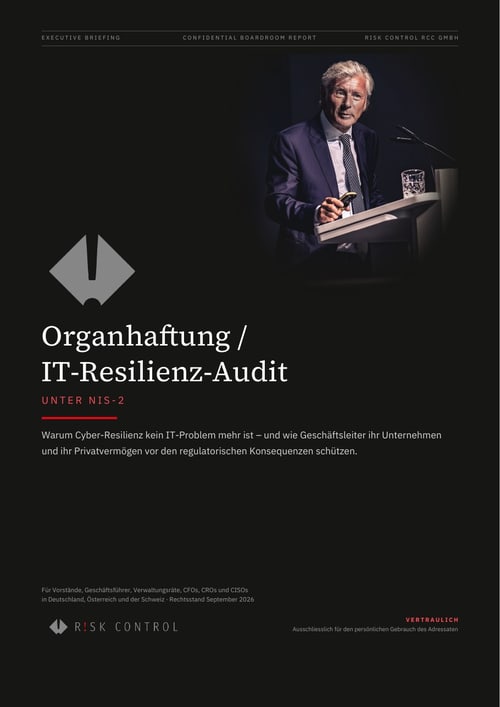
              Executive Briefing: directors’ liability and IT resilience audit
              NIS-2 Executive Intensive
              NIS-2 Article 20 · Personal liability of management (in German)
              Executive Briefing: Directors’ liability / IT resilience audit
              Executive Briefing · PDF (in German)
              Crisis Bootcamp29 Jan 2027 – register (in German)